
Unified Intelligence. Coordinated Action. One Operational Picture.
The Challenge
Security teams don’t lack tools. They lack alignment. Most organizations operate across:
- Separate SIEM environments
- Disconnected SOAR workflows
- Standalone ticketing systems
- Isolated scanners and sensors
- Fragmented intelligence feeds
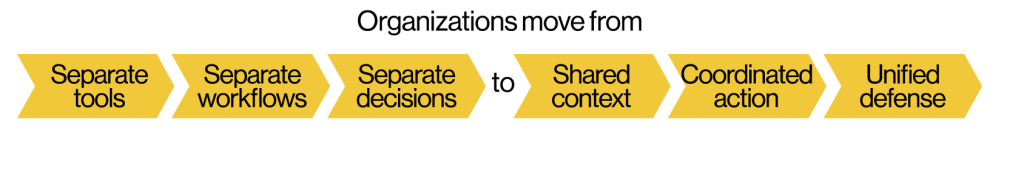
The result: Each team sees part of the threat landscape, but no one sees the full picture – leading to duplicated effort, inconsistent response, and operational drag.
The Analyst1 Difference
Analyst1 connects intelligence, systems, and teams into a shared operational fabric. Instead of piecing together content across platforms, Analyst1 ensures everyone works from the same enriched, real time intelligence foundation.
How It Works
Analyst1 enables true operational alignment through four core capabilities:
- Shared Intelligence Context
- Deep Tool Integration
- Cross-Team Workflow Coordination
- Consolidated Case & Operational Visibility
What Analyst1 Delivers
- Alignment
- Precision
- Resilience
- Efficiency
- Scale
Other solutions were piecemeal. Analyst1 is more than a TIP. It refines our caseload in ServiceNow and gives us far more value from our intelligence… We’re going to consolidate so much effort in here.
– CTI Lead, Global Financial Institution
Why It Matters
| Without Analyst1 | With Analyst1 |
| Disconnected tools | Integrated security stack |
| Siloed teams | Coordinated operations |
| Duplicated analysis | Shared intelligence context |
| Manual reconciliation | Automated alignment |
| Fragmented visibility | Unified operational picture |
Operating as One isn’t just integration – it’s operational unity, where every team, tool, and decision is connected by shared intelligence.
The Bottom Line – Threats exploit gaps between systems and teams. With Analyst1, your intelligence tools, and people operate as one.
About Analyst1
Threat intelligence teams often struggle to bridge the gap from insight to action. Analyst1 is the Operationalized Threat Intelligence Platform designed to resolve this issue. It automatically organizes threat data, links it to your assets and vulnerabilities, and customizes views for different roles. Analyst1’s centralized layer streamlines workflows and automates reliable actions by integrating with SIEM, ticketing, and vulnerability management systems. From Fortune 500 financial institutions to national security agencies, enterprises trust Analyst1 to unify their defenses, significantly reducing their response time from days to minutes.