Turn threat intelligence to action,
on any network
Analyst1 gives CTI, SOC, vulnerability, threat hunting, and IR teams one operational view, turning intelligence into detections, tickets, and mitigations. Deploy it in the cloud, on-prem, or on classified and air-gapped networks.
Trusted by Fortune 500 enterprises and national security agencies

You’re Drowning in Intel,
But Are You Any Safer?
Does this sound familiar?
Your intelligence team produces valuable insights, but you can’t track if anyone acts on them.
Your detection team writes rules, but they often lack the broader context your intel team has already uncovered.
Your response teams spot suspicious activity but are left to figure out if it’s a known threat or part of a larger campaign.
Your vulnerability team has a mountain of exposures to patch, with no clear way to prioritize based on active threats.
Each team is doing its part, but the effort is fragmented.
This creates a “Threat Coordination Gap,” where known threats can go unblocked, uninvestigated, and unpatched.
It’s time to operationalize your defense.
The value of threat intelligence isn't just knowing about threats; it's ensuring the right people take the right actions to stop them.
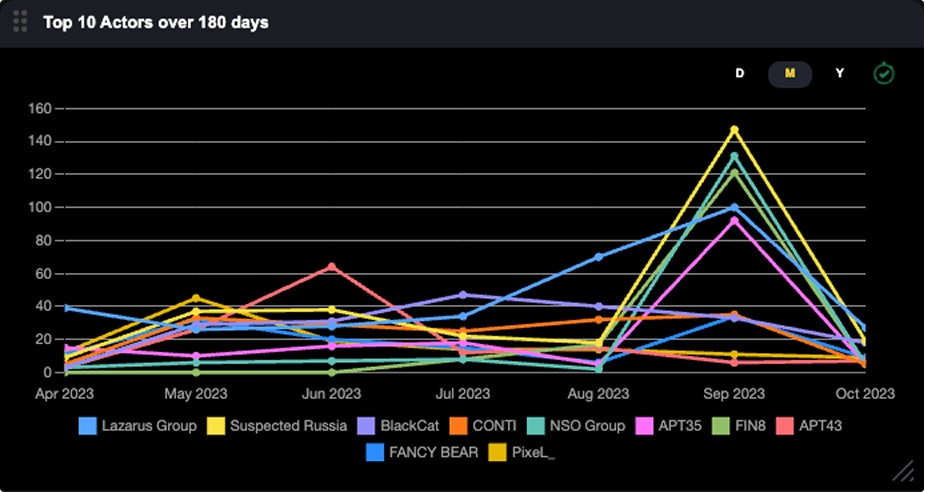
Analyst1 was built from the ground up to solve the Threat Coordination Gap. More than a repository or a platform to manage intelligence, Analyst1 is an operationalized layer that connects your intelligence to outcomes. We integrate your systems, automate workflows, and provide a shared picture of your environment so you can finally operate as one unified defense.
How Analyst1 Turns Intelligence into Action
1.

Get Tailored, Actionable Intelligence
Stop sorting through a noisy inbox of raw feeds and unstructured reports.
Analyst1 automatically extracts and structures threat data, from indicators and malware to TTPs and targeted victims. It then tailors everything—scoring, dashboards, and data layouts—to the way your team thinks and prioritizes risk, ensuring every role gets the exact intelligence they need.
2.
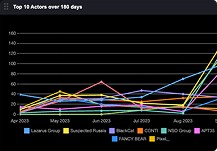
Operate as a Single, Unified Defense
Break down the silos between your teams and tools.
Analyst1 connects your SIEM, SOAR, scanners, and ticketing platforms, creating a unified mesh where intelligence, systems, and people work in concert. Threat context is pushed into SIEM alerts, vulnerability scans are linked to the actors that exploit them, and every team works from the same, up-to-date picture.
3.
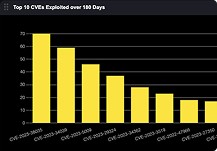
Minutes to Mitigation, Not Days
Shorten the distance between knowing and doing.
With Analyst1, you define trusted actions that automatically trigger a block, open a ticket, or escalate a vulnerability based on clear, codified policies. Our orchestration engine executes the response the moment a threat is identified—no need to pivot between tools or wait for manual intervention.